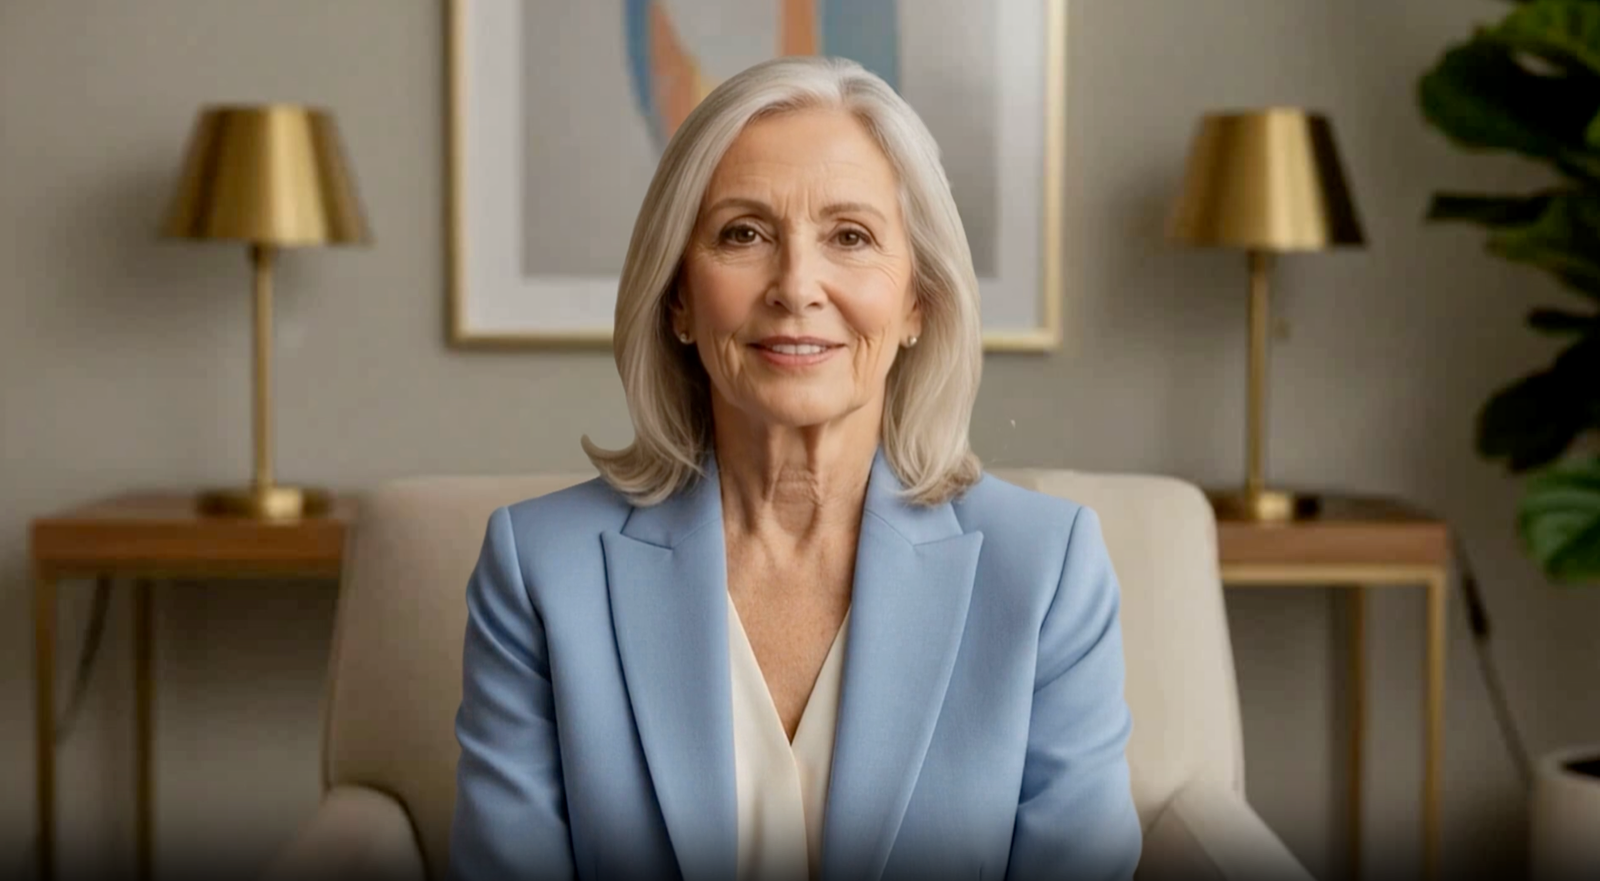
CYmantha is a Cyber Cube Companion: a conversational AI persona who listens, speaks, and keeps you company. Ask her anything, by voice or text, any time.
CYmantha speaks for a real organization: a fully de-identified company profiled by CyberCube, the cyber risk analytics platform used by insurers, brokers, and security teams. Everything she knows comes from that profile, so the conversation works best when you know who you are talking about, and which seat you are sitting in.
Beyond this company's risk profile, CYmantha's knowledge base carries CyberCube's full public site: the products behind this analysis, including Broking Manager and Account Manager, along with the company's services, methodology, and point of view. Ask her what a product does, how a score is built, or where any number in this briefing comes from.
The short version: a modern cloud company with serious hygiene problems. Strong multi-cloud footprint on AWS and Google Cloud, managed devices through Intune, MFA through Azure AD and Okta, excellent SSL hygiene. But end-of-life software sits in the bottom 1% of the entire market, network misconfigurations have been stuck near the 2nd percentile for twelve straight months, and scanners see active infection indicators, exposed services, and leaked credentials in dark web data dumps. No SIEM, no observable backup solution, no dedicated email security: fundamental gaps for a healthcare organization handling protected health information.
CYmantha opens by asking what seat you hold. Pick one from the cards below and stay in character: she calibrates depth, vocabulary, and priorities to the role you choose.
Risk scores and percentile ranks, the individual security signals, the twelve month trend, financial loss modeling, the ransomware cost breakdown, peer insurance benchmarks, and where remediation should start.
She speaks to this one company's profile. General cyber questions land best when you tie them back to what the scan actually found: "we have no SIEM, what should detection look like for us?"
These are the executives who would sit in this briefing in real life, drawn from ISO/IEC 27001 and ISO 31000 governance structures, the NIST Cybersecurity Framework, and the HIPAA Security Rule. Tell CYmantha which one you are, then ask what that person would ask.
"Which control gaps would you close first, and what order actually reduces risk?"
"Exposure is 97th percentile, security is 76th. How do I frame that gap for the board?"
"What does our detected stack say about our patching and configuration discipline?"
"Walk me through legal liability and regulatory cost in a 95th percentile ransomware event."
"Peers carry $13M in limits. What should we buy, and what does the loss curve justify?"
"Which findings put protected health information most at risk today?"
"Would you write this risk today? Price the hygiene problems for me."
"What three questions should we put to management this quarter?"
The underlying company is fully de-identified: names, domains, and identifying details have been removed from CYmantha's knowledge. The role list follows ISO/IEC 27001, ISO 31000, NIST CSF, and HIPAA governance structures; organizations adopting AI systems can map the same seats to ISO/IEC 42001 oversight roles.
CYmantha is a Cyber Cube Companion. She listens, she speaks, and she holds a real conversation. Click her card below to start talking.
A Cyber Cube Companion you can have a real conversation with.
CYmantha is a Cyber Cube Companion: an Interactive Avatar built for conversation. She looks and sounds like a person on a video call, listens as you speak, and responds in kind, in her own voice. Ask her about her day, talk through yours, or just see what she has to say. By voice or by text, she is available whenever you are.
CYmantha is a demonstration persona, not a real person.
No signup. No form. Voice or text. Available any time.